Shopify Privacy, Cookies, and Consent: Start with Four-State Testing
16 parts · 2 checkpoints
Show all 16 parts
- 01First decision
- 02Term notes
- 03Consent nodes
- 04Four layers
- 05State testing
- 06Vendor Script Inventory
- 07Customer rights requests
- 08Escalation conditions
- 09Consent conflict check
- 10Pause/continue rule
- 11Reporting reuse
- 12Turn the check into a reusable conclusion
- 13Quick Check, has a checkpoint
- 14Consent pressure-check practice
- 15Consent evidence record
- 16Compliance paths after privacy and consent review
If your Shopify store uses pixels, GA4, email popups, or remarketing, test four states first: first visit, reject, accept, and withdrawal. Record which scripts run, which data supports ads or analytics, and who handles customer requests; then choose continue, test small, pause, or escalate.
This lesson answers
First decision
Whether the user agrees decides what data you can collect and use.
A cookie popup by itself does not complete consent governance. Check which scripts must not collect before consent, which data may support analytics, ads, email, and remarketing after consent, and which actions must stop after withdrawal. Keep the actual request, data purpose, recipient, and regional branch in one evidence line. This is an operating check, not legal or privacy advice for a particular market. When evidence is incomplete, pause the action that would expand collection, audiences, or outreach. Do not use one green admin check or one reporting drop instead of four-state testing.
Consent evidence record
Acceptance: page disclosure, script firing, consent state, event gaps, customer rights, and vendor inventory can answer what may be collected, what may be used, and who reviews it.
- Page layer: Whether visitors can understand data use, choice, withdrawal, and opt-out path.
- Tag layer: Whether marketing, analytics, and functional scripts fire correctly under each consent state.
- Reporting layer: Whether consent rate, event gaps, modeled data, and remarketing audience changes are explained correctly.
- Change layer: Whether new apps, pixels, email tools, or data-sharing settings trigger review.
Term notes
Define consent, consent tools, and reporting signals first.
A cookie banner is the interface for visitor data choices. It is only the entrance; governance depends on whether scripts and events change after the choice. Example: If Meta or Google marketing tags fire before the visitor chooses, the banner is not a working consent gate.
- Consent state
Consent state is whether the visitor has granted, rejected, not chosen, or withdrawn consent. It affects ads, analytics, remarketing, email, and reporting. Example: After rejection, marketing events should be suppressed; after acceptance they resume; after withdrawal, later visits should not use the old state.
- Customer Privacy API
Shopify Customer Privacy API reads, updates, and listens to customer privacy preferences. If a third-party banner, custom pixel, or app does not wait for the API and listen to asynchronous consent events, choices and script behavior can drift. Example: Testing should check whether analytics, marketing, preferences, and sale-of-data permissions are read correctly.
- Feed
A feed is the product data file sent to ad or commerce platforms with product, price, inventory, URL, and policy signals. Here, feed matters because ad platforms connect product data, page behavior, and remarketing audiences in one growth chain. Example: If the feed promotes EU products while the page does not explain duties, privacy choices, and tracking boundaries, the issue is not only product data.
- Checkout
Checkout is where the buyer confirms the order, pays, enters address details, and sees final promises. Consent governance checks whether checkout aligns with privacy policy, email consent, duties copy, and data-sharing choices. Example: If checkout preselects marketing subscription or blurs order notifications with marketing email, it needs consent review.
- Google Consent Mode v2
Google Consent Mode v2 helps Google tags handle consent state. In addition to ad_storage and analytics_storage, check ad_user_data and ad_personalization because they affect advertising user data, personalized ads, modeled data, and conversion reporting interpretation. Example: For EEA visitors, consent state must be passed correctly for personalized advertising; reporting drops can be consent-boundary effects, not business decline.
- Customer rights request
Customer rights requests include access, correction, deletion, opt-out, and unsubscribe. Support, operations, technical teams, and app owners may all be involved. Example: If deletion requests land in an inbox with no assigned owner, the decision is pause, not adding more pixels.
- Vendor script inventory
Vendor script inventory lists apps, pixels, popups, heatmaps, reviews, affiliates, and data recipients. Update it whenever a tool is added. Example: After adding an email popup tool, record what it collects, who receives it, and whether consent controls it.
Consent nodes
Do not only inspect the banner; inspect whether each node is controlled.
Privacy governance puts pages, scripts, consent states, events, customer rights, and vendors in one table. Choose one node, check its evidence and pause signal, then write the result into the final consent evidence record.
Use a node to trace a specific data path, rather than only naming a tool. Each path needs its data class, processing purpose, recipient, and regional branch. Storefront promise, actual request, vendor record, and assigned owner must be cross-checkable. One banner does not grant the same processing permission to every vendor. Write the first gap into the record before deciding whether to pause. Do not skip other data paths because one node looks green.
The four-state test has a research basis, but the study does not replace a current compliance assessment. In Dark Patterns after the GDPR: Scraping Consent Pop-ups and Demonstrating their Influence, the study examined five targeted CMP vendors across the top 10,000 UK websites during three scrape days in September 2019. Among 680 successfully scraped CMP instances, only 11.8% met all three operationalized minimum conditions at once: explicit consent, equally easy Accept All and Reject All actions, and no optional boxes pre-ticked. The data appears on PDF p. 5, Table 1; here we use the CHI 2020 proceedings / arXiv v1 author version. The result is a historical benchmark for the paper’s testable subset, not a current legal compliance rate, today’s platform audit, or conversion performance. Current law and platform requirements remain anchored to the regulator and the official sources listed at the end of this lesson. Across first visit, reject, accept, and withdrawal, record the expected and actual consent state, whether each script or event fired, its purpose and recipient, the timestamp, and the page or configuration version. If a non-essential request still fires after rejection or withdrawal, or the log cannot connect the state change to the request, pause new pixels, audiences, or outreach and record the assigned owner and recovery condition.Consent Verification Monitoring describes a way to check changes in consent state and monitor the log. It records grants, withdrawals, purposes, recipients, and collection or access events, then checks whether later policy changes preserve or revoke earlier interpretations. The paper uses a formal model, runtime-monitor architecture, scripted scenarios, and a constrained simulation to demonstrate the method. It is not a production-merchant deployment, legal certification, or proof that Ecomwith is compliant. Here we use it only to shape consent-state/logging fields. The cited source is ACM TOSEM 2023 / repository manuscript; the architecture appears on PDF pp. 4-6, the constrained simulation and complexity evaluation on pp. 19-22, and the integration and enforcement boundary on p. 28.
Which consent node first?
Tap one node; the right side changes to the matching check. On mobile, just tap the card.
- Check
- Whether privacy policy, cookie banner, preferences, and opt-out page explain data use.
- Evidence
- Mobile page records, privacy policy, cookie copy, preferences page, data sharing opt-out page.
- Pause signal
- Copy says visitors can choose, but withdrawal or opt-out path is missing.
- Owner
- Operations / legal coordination lead
- Check
- When Meta, Google, affiliate, heatmap, popup, and review scripts fire under each consent state.
- Evidence
- Network, Tag Assistant, Pixel helper, GTM preview, browser storage.
- Pause signal
- Non-essential marketing tracking fires before choice or after rejection.
- Owner
- Technical / data lead
- Check
- Whether first visit, reject, accept, withdraw, or opt-out states are recorded clearly.
- Evidence
- CMP state, Customer Privacy API state, event log, consent update time.
- Pause signal
- Storefront shows rejection, but API or tags still process as consented.
- Owner
- Data / technical lead
- Check
- Whether GA4, ad platforms, remarketing audiences, and conversion reports label consent impact.
- Evidence
- GA4 DebugView, ad diagnostics, consent rate, modeled data notes, drop records.
- Pause signal
- Reporting drop is treated as business decline without checking consent-boundary changes.
- Owner
- Data / ads lead
- Check
- Who handles access, correction, deletion, opt-out, unsubscribe, by when, and where records live.
- Evidence
- Support handling steps, inbox rule, admin flow, request log, response template.
- Pause signal
- Before adding new collection tools, customer requests have no assigned owner or response timing.
- Owner
- Support / operations lead
- Check
- Whether all apps, pixels, scripts, and data recipients have an inventory and review cadence.
- Evidence
- Shopify app list, GTM container, pixel list, email tools, heatmap and review tool settings.
- Pause signal
- New app or pixel added without updating policy, inventory, or consent tests.
- Owner
- Technical / operations lead
Four layers
Review page, tags, reporting, and changes together.
Only checking the page is risky because visitor-facing promises can diverge from script behavior. Four-layer governance aligns choice, firing, reporting, and change records.
Choose a case: Page layer
- Job
- Whether visitors can understand data use, choice, withdrawal, and opt-out path.
- Evidence
- Privacy policy, cookie banner, preference page, opt-out page, mobile page record.
- Failure mode
- The page implies choice, but no usable preferences entry exists.
- Job
- Whether marketing, analytics, and functional scripts fire correctly under each consent state.
- Evidence
- Network, GTM preview, Tag Assistant, Pixel helper, Customer Privacy API return values.
- Failure mode
- Banner appears, but non-essential scripts already sent requests before consent.
- Job
- Whether consent rate, event gaps, modeled data, and remarketing audience changes are explained correctly.
- Evidence
- GA4, Google Ads, Meta, CMP, and Shopify analytics anomaly records.
- Failure mode
- Misreading consent-driven data gaps as ad or page performance decline.
- Job
- Whether new apps, pixels, email tools, or data-sharing settings trigger review.
- Evidence
- Vendor inventory, change log, review date, assigned owner, rollback condition.
- Failure mode
- A script is published in GTM or an app without privacy review.
State testing
Consent QA must inspect firing order.
Do not write only that the banner works. Minimum testing covers first visit, reject, accept, withdraw or opt-out, with state records, timing, state, assigned owner, and review date.
Run the consent lifecycle as a test sequence with readback. Confirm the default state, then record the updated state after the visitor actually chooses. First visit, reject, accept, and withdrawal must each point to an actual request or state record. Regional settings can differ, so one market’s default cannot stand in for every visitor. After withdrawal, retest later visits rather than only checking that a settings toggle is visible. Do not keep the old state and treat a new visitor choice as handled.
Choose a case: First visit, no choice
Network / Tag Assistant / Pixel helper / storage.
Cookie storage, GA4/Meta events, CMP state.
Event recovery, consent state, ad-platform debugging.
Preferences page, opt-out page, later events, request log.
After a visitor rejects, accepts or withdraws, what should each marketing tool do?
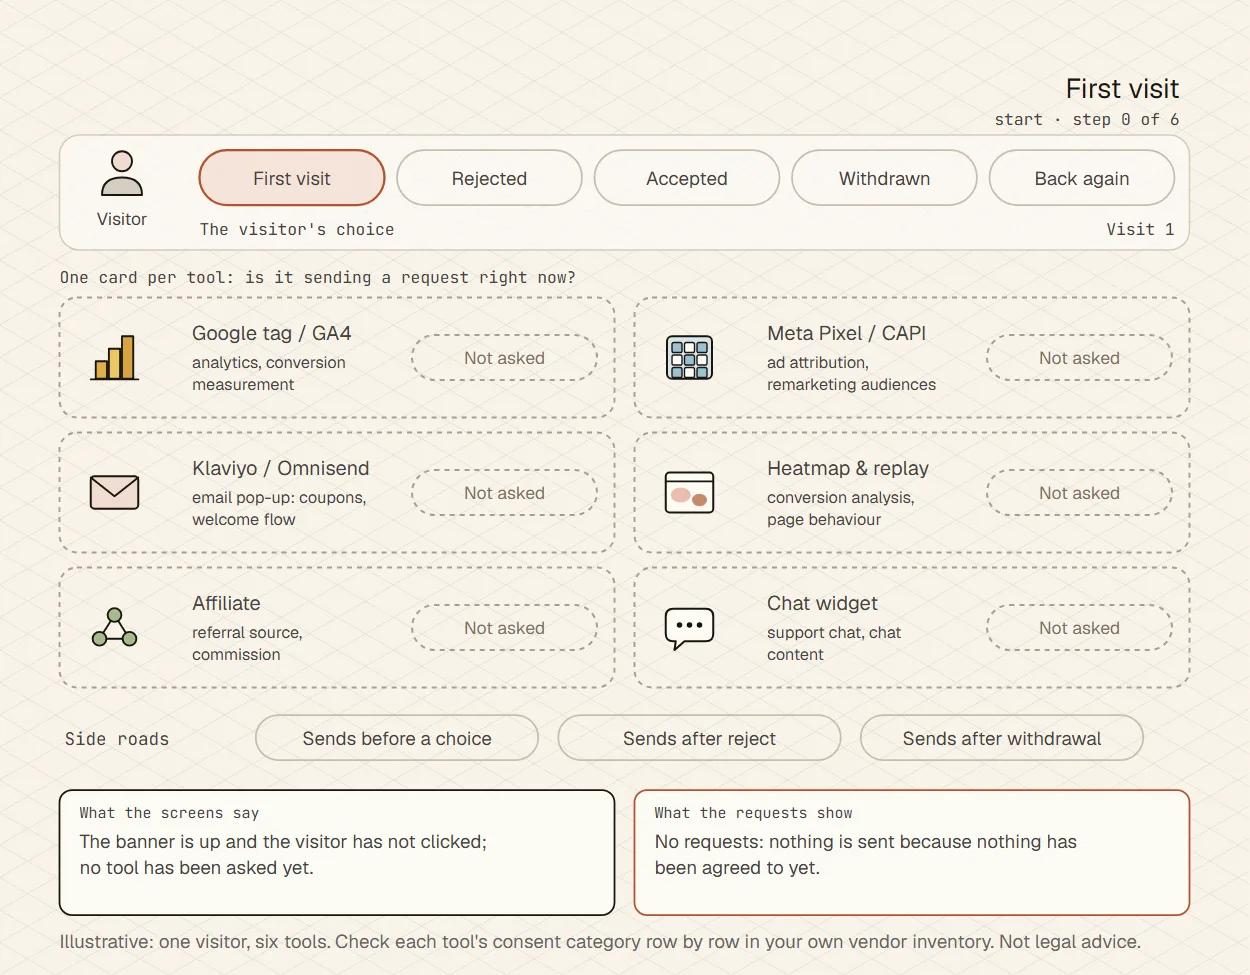
As text: the whole walk-through
- Accepted The visitor accepts, and only now may the tools start sending requests.
- Withdrawn The visitor withdraws in the preference page and the requests should stop; the next visit has not been tested yet.
- Sent after withdrawing The visitor comes back and Meta reuses the old "accepted" and sends again, while the preference page still shows the switch off.
- Sent after withdrawing Check how the Customer Privacy API is read, so the tag reads the current consent state on every visit.
- Back, still quiet Visiting again and reading the actual requests: Meta is back to quiet, so the withdrawal holds on later visits.
- Retest passed Requests, consent state and time go into one record, and only then is the withdrawal tested.
Illustrative: one visitor, six tools. Check each tool's consent category row by row in your own vendor inventory. Not legal advice.
Vendor Script Inventory
Five steps to land privacy consent
List consent nodes
When page, checkout, email, and support each need consent.
How to confirm
Write what happens after a decline at each node.Inventory vendor scripts
Who loads, what they read, where data goes, and whether they can be turned off.
Keep as evidence
Keep the script list and screenshots.Test the decline path
Buying, refunds, and support must still work after tracking is declined.
Caution
Testing only accept paths misses real shoppers.Handle rights requests
Access, deletion, and correction need an entry point, deadline, and owner.
How to confirm
Request record and completion time read back.Write review and escalation
Pause the affected script on conflict or complaint, then escalate to the owner.
If it goes wrong
Do not cover old scripts with a new consent banner.
Before adding an app, pixel, or popup, record what it collects and who receives it.
Consent checks often fail when a new tool ships without entering the inventory. Each row should answer purpose, data, recipient, whether it loads before consent, consent category, rollback owner, and last checked date.
Use the vendor inventory to keep the data-flow map reviewable. Before adding a tool, establish its processing purpose and controlled state instead of documenting it after launch. Keep tool, fields, recipient, trigger condition, and last-check material on one line. This inventory locates data flow; it does not decide legal permission for a particular market. When the recipient is unclear, freeze the new sync or audience it creates. Do not treat installing an app as completing vendor governance.
Row by row: purpose, data, recipient, consent control, evidence
GA4 / Google tag
- Purpose
- Analytics, conversion measurement, and Consent Mode signal passing.
- Data
- Page views, events, order events, and ad_storage / analytics_storage / ad_user_data / ad_personalization state.
- Recipient
- Google / GA4 / Google Ads.
- Consent control
- Record default value, update value, GTM trigger, four-state tests, and whether it loads before consent.
- Proof
- Tag Assistant, GA4 DebugView, Network, GTM publish time, last checked date.
Meta Pixel / CAPI
- Purpose
- Ad attribution, remarketing audiences, and event quality.
- Data
- Browser events, purchase / add_to_cart, possible user parameters, and audience sync state.
- Recipient
- Meta and ad dataset.
- Consent control
- Check firing before consent, suppression after rejection, recovery after acceptance, and no reuse after withdrawal.
- Proof
- Network, Pixel helper, Customer Privacy API state, audience sync note.
Email popup / Klaviyo / Omnisend
- Purpose
- Coupon delivery, welcome flow, marketing email, SMS, or audience sync.
- Data
- Email, phone, form source, marketing permission, unsubscribe and deletion state.
- Recipient
- Email or SMS platform, ad audience sync destination.
- Consent control
- Separate coupon delivery, order notices, marketing outreach, double opt-in, unsubscribe, and deletion path.
- Proof
- Form version, field mapping, welcome-flow trigger, unsubscribe page, support request template.
Review, heatmap, session replay, affiliate, chat widget
- Purpose
- Conversion analysis, review display, referral commission, support chat.
- Data
- Page behavior, device or browser data, session records, referral source, chat content.
- Recipient
- The app or third-party service provider.
- Consent control
- Before launch, record whether it loads before consent, consent category, rollback owner, and privacy-policy update.
- Proof
- Shopify app list, Network, script inventory, vendor note, change record.
Customer rights requests
Deletion, unsubscribe, and opt-out requests cannot stop in the support inbox.
Treat a customer rights request as a process drill: it exposes whether Shopify admin, email platforms, ad audiences, vendors, and support response can close the loop. Any step without an owner pauses new data collection.
A data-subject request (DSAR) practice restates a cross-system path; it does not process customer data. Separate access, correction, deletion, unsubscribe, and opt-out before confirming the intake and escalation route. Record request type, reviewable system path, vendor response, and any remaining gap. This local practice does not create, read, or modify real customer, order, account, or vendor records. When no assigned owner can confirm and track a step, pause new collection and escalate to the appropriate lead. Do not write “request completed” merely because someone replied.
Row by row: Action, Evidence
| Item | Action | Evidence |
|---|---|---|
| Intake request | Mark source, request type, market, email or order ID; do not merge deletion, access, unsubscribe, and opt-out into one support issue. | Ticket, original email, request time, support owner. |
| Verify identity and admin path | Confirm whether the user can be found in Shopify admin, customer profile, order records, email platform, and SMS platform. | Admin screenshot or record path, assigned owner, record ID when screenshot is not allowed. |
| Sync vendor handling | Confirm deletion, unsubscribe, or opt-out path for email, ad audience, review, heatmap, affiliate, chat, and other vendors. | Vendor confirmation, action time, reason if deletion is impossible, escalation target. |
| Respond, log, and escalate | Record response timing, completed scope, incomplete scope, and next review trigger; if it cannot close, move into incident response. | Response template, handling log, last checked date, escalation path. |
Escalation conditions
These cases need legal or privacy escalation, not more tutorial judgment.
This material is not legal advice. It helps the team record evidence, assigned owners, and pause lines; sensitive data, transfers, vendor contracts, unresolved requests, or incidents need escalation.
Row by row: Condition, Pause line
| Item | Condition | Pause line |
|---|---|---|
| Item 1 | Large EU/EEA advertising, remarketing, lookalike export, or unclear cross-border data transfer boundary. | Do not expand audience sync or new-market ads before legal/privacy review. |
| Item 2 | Children, health, sensitive category, SMS permission, email permission source, or unclear vendor DPA. | Freeze new collection and marketing automation until permission source and vendor boundary are clear. |
| Item 3 | Deletion, access, opt-out, unsubscribe request cannot be handled, or vendor deletion path cannot be confirmed. | Stop adding data recipients and escalate to support, operations, technical, and privacy leads. |
| Item 4 | Missent data, breach, regulator/platform warning, or continued marketing firing before consent. | Move into high-risk incident response; do not treat it as a normal tag or copy issue. |
Consent conflict check
Read banners, pixels, email, and reports inside one conflict case.
The three conflict cards below are clickable: pick the one that looks most like your situation, and the selected card explains how to trace a visible symptom back to the hidden conflict.
Choose a real conflict
Do not only ask whether a banner exists. Ask which growth action this conflict makes unreliable.
- Trigger
- Operations adds a 10% off email popup. After signup, the user enters the welcome flow, but the popup does not separate discount delivery, order notices, and marketing email.
- Visible symptom
- Subscribers rise, so the team wants to expand welcome flows, abandon flows, and remarketing audiences immediately.
- Hidden conflict
- Email consent, privacy policy, form copy, and automation triggers do not match, and unsubscribe or deletion requests are not closed-loop.
- First test
- Run one test signup and check form copy, email-tool fields, double opt-in setting, unsubscribe link, and deletion request path.
- Evidence pack
- The evidence pack needs form version record, subscription fields, welcome-flow trigger, unsubscribe page, support request template, and vendor inventory.
- Fix order
- Fix form consent copy and field mapping first, then update privacy policy and vendor inventory, then restore automated emails.
- Reporting note
- Email growth should split marketable subscribers, discount-only signups, unsubscribes, and invalid addresses, not only total signups.
- Freeze rule
- Freeze new welcome flows, SMS, remarketing sync, and lookalike exports while marketing consent is unclear.
- Consent evidence record
- node=unclear email popup consent; scope=discount popup/welcome flow/remarketing sync; evidence=form version, subscription field, unsubscribe page, support template, vendor inventory; assigned owner=email lead; last verification date=2026-10-03; escalation=email and privacy leads when marketing consent is unclear.
- Trigger
- After the team fixes Consent Mode v2 and the banner, GA4 purchases, Google Ads conversions, and Meta events drop at the same time.
- Visible symptom
- The meeting immediately blames ads, landing page quality, or creative fatigue.
- Hidden conflict
- Visibility changes are misread as business changes; ad_user_data, ad_personalization, analytics_storage, or pixel firing changes can shift reports.
- First test
- Compare Shopify orders, consent rate, Consent Mode parameters, GA4 DebugView, Tag Assistant, and ad-platform diagnostics first.
- Evidence pack
- The evidence pack needs fix date, changed settings, whether orders also dropped, consent-rate change, event gap, and modeled-data note.
- Fix order
- Add reporting-definition notes first, then decide whether ads or pages need action; do not use budget to fix a visibility gap caused by consent.
- Reporting note
- The weekly report should separate real orders from visible conversions and state that platform conversion counts are not directly comparable to last week.
- Freeze rule
- Do not cut budget or rebuild pages only because visible platform conversions drop while orders do not drop.
- Consent evidence record
- node=reporting drop after consent repair; scope=GA4/Ads/Meta/Shopify orders; evidence=fix date, consent rate, Consent Mode fields, DebugView, Tag Assistant, real orders; assigned owner=data lead; last verification date=2026-10-03; escalation=weekly reporting note when visible conversions diverge from real orders.
Pause/continue rule
Decline path not tested
| Stop here | Go |
|---|---|
Do not launch or scale before buying, refunds, and support work with tracking declined. | Walk the decline path once and record each step before continuing. |
| Evidence Decline-path screenshots and notes. | |
Vendor scripts unknown
| Stop here | Go |
|---|---|
Do not enable marketing or analytics scripts while data readers and destinations are unknown. | Complete the script list, purpose, and opt-out, then decide. |
| Evidence Script list and vendor documentation. | |
No rights-request entry
| Stop here | Go |
|---|---|
Do not claim compliance while access, deletion, or correction requests lack an entry point and owner. | Set the request entry, deadline, and record before making public claims. |
| Evidence Request entry, handling record, and owner. | |
Not every data drop means business got worse.
Consent governance affects GA4, remarketing, email lists, heatmaps, and support requests. The pause/continue rule separates real business issues from consent-boundary changes.
- Banner exists, but non-essential scripts fire early.: Pause: fix trigger order before launch.
- New ad pixel added without inventory update.: Pause until documented: update inventory, policy page, and test records.
- Consent-rate change shifts reporting.: Continue with reporting note: label consent boundary in reports.
- Customer rights requests have no assigned owner.: Pause new data collection: assign an owner, document the handling steps, and set a response deadline.
Reporting reuse
Write consent decisions back into GA4, ads, and weekly reporting.
The privacy checklist is only the starting point. The business value comes when consent rate, event gaps, modeled data, and visible-conversion changes enter reporting definitions, so ads, CRO, and email teams know when to change pages and when the issue is only consent scope.
Row by row: Decision, Reuse
| Item | Decision | Reuse |
|---|---|---|
| GA4 Consent Mode fields | Record whether ad_storage, analytics_storage, ad_user_data, and ad_personalization change by region and visitor choice. | Reuse in the GA4 Consent Mode lesson as the tag setup and DebugView review condition. |
| Event gap and real orders | Compare Shopify orders, GA4 purchase, Google Ads conversions, and Meta events to separate visible-data shifts from business shifts. | Reuse in event QA and weekly notes before cutting budget because visible platform conversions dropped. |
| Remarketing and email consent | Separate marketable subscribers, discount-only signups, unsubscribes, deletion requests, and remarketing audience sync state. | Reuse in ad audiences, welcome flows, and support request records so unclear consent does not enter outreach. |
Open these internal links when continuing
- EU boundary and GPSR: align entity, policy pages, tax and parcel scope first.
- Market-entry risk: pass the risk gate before touching budget.
- Payments and settlement: how display price, charge and payout differ.
- Event quality check: confirm the event still fires after consent states change.
If you are fixing reports, tags, or budget judgment, do not stop here by instinct. Carry this consent-state record into the workflows below.
Turn the check into a reusable conclusion
Judge consent by data path, then hand the result to operations.
Translate the facts from state tests and conflict cases into pause, recovery, and responsibility-assignment actions. One green admin status or platform event is not enough to continue.
Before turning state tests into operating action, name the data path that changed. Only when default, update, regional branch, and post-withdrawal result are connected does a reporting shift have an explainable boundary. Put orders, consent rate, event gaps, vendor records, and customer requests on one timeline. This organizes evidence; it does not replace technical implementation or specialist advice. Write the pause scope and recovery condition before passing the conclusion to ads, email, or data leads. Do not reopen a path that should stay suppressed simply because visible conversions fell.
Temporary approval still needs a boundary
The minimum record is not a note saying checked. It is the governance record below: review scope, data purpose, script list, consent-state test, reporting boundary, owner, pause or continue, governance map, vendor and customer rights, legal escalation. A reviewer can immediately see which field is still blank.
Bounded temporary approval
When evidence is incomplete, temporary approval must be limited by traffic, market, or SKU and must include a due date. The goal is not day-one perfection; it is to keep unfinished work inside a recoverable scope.
Recovery is not data that looks normal
All four consent-state results match the expectation.
Form fields and unsubscribe paths align.
The missing recipient is restored to the vendor inventory.
The weekly report separates modeled events from visible events.
- Data existence and use boundary: Separate receiving data from being allowed to continue outreach. In one visit, order-notice records, form fields, analytics events, marketing audiences, and vendor sync can all appear. One valid record does not authorize every other path for analytics, remarketing, or email. Keep the data class, recipient, visitor choice, and next action on one line so “data exists” is not misread as “data may be used.”; A discount form on a 20oz tumbler page can easily blur coupon delivery with marketing permission. If a marketing request appears on first visit or events remain visible after rejection, record the page, tool, and visitor state; freeze only the action that expands new data or audiences instead of relying on a banner or one green admin check to keep spending. For first visit, reject, accept, and withdrawal, record the expected result, actual firing, and assigned owner one state at a time. Place the issue in the page, tag, reporting, or change layer so a visible symptom does not go to the wrong owner. Write the pause scope and recovery condition in the evidence record before restoring ads, audiences, welcome flows, or a new form.
- How to make the result reviewable: Explain measurement scope before judging growth, and make the record reviewable. When GA4, ad-platform, or remarketing counts fall, read Shopify orders, consent rate, event gaps, modeled data, and customer requests over the same period. Investigate budget or page optimization only if orders, customer feedback, or fulfillment facts move in the same direction; otherwise the weekly report should name the consent boundary instead of reopening a path that should stay suppressed for prettier conversions. Run an independent review: ask someone who did not run the test to restate the four states, which tool is still at risk in the current market, what is paused, where the evidence lives, and what restores it. If the answer depends on one technical teammate’s memory, the checklist is not yet an operable consent evidence record. Mark the market, date, and consent-state change first, then read order, event, and audience shifts side by side. Separate visible-data changes, confirmed business changes, and unexplained gaps instead of deciding from one total conversion number. Run an independent review; if it cannot confirm the path, add the assigned owner, evidence location, or recovery condition before adding more collection.
Quick Check
A banner does not mean scripts are controlled.
Your site has a cookie banner, but on first incognito visit Tag Assistant shows a marketing tag fired already. The team says "the banner exists, launch first." What is the safest decision?
Self-check: choose before reading feedback
Self-check not answered
What comes first in this consent check?
Note
Pick a move first
Pause the conflicting script first
This move scales the risk
Consent pressure-check practice
Consent mistakes happen when business pressure makes the team accept surface-level proof.
Privacy work is often misread as "banner exists, so done." In practice, banners, reports, apps, and customer requests expose different evidence gaps under pressure. Choose a pressure scenario, then write the first evidence, allowed move, and freeze rule into the consent evidence record.
Pick a consent pressure
Do not ask launch first. Ask which evidence layer this pressure is trying to skip.
- Pressure scenario
- Reporting drops, and the meeting immediately blames ads or the landing page.
- Tempting move
- change budget, bids, or the page immediately.
- Safer read
- first check whether cookie banner, Consent Mode, GTM, pixels, or data-sharing settings changed.
- First evidence
- Compare consent rate, event gaps, Tag Assistant diagnostics, GA4 DebugView, and ad-platform diagnostics first.
- Allowed move
- If it is a consent-boundary change, annotate reporting definitions before touching budget.
- Freeze rule
- Do not treat data loss as business loss until consent state is verified.
- Consent evidence record
- scope=GA4/Google Ads/Meta reporting; states=consent rate and four Consent Mode fields before/after repair; evidence=DebugView, Tag Assistant, real Shopify orders; assigned owner=data lead; last verification date=2026-10-03; escalation=update reporting notes when orders hold but platform conversions drop.
- Pressure scenario
- Operations wants to add an email popup, review tool, heatmap, or affiliate script immediately.
- Tempting move
- judge only conversion upside and skip the vendor script inventory.
- Safer read
- every new tool adds a data recipient, trigger condition, and customer promise.
- First evidence
- Write what it collects, who receives it, whether consent controls it, and whether the privacy policy needs updating.
- Allowed move
- Ship the tool only after inventory, policy page, state tests, and rollback owner are recorded.
- Freeze rule
- Do not publish a new script without an inventory entry, test records, and a named owner.
- Consent evidence record
- scope=new popup/review/heatmap/affiliate tool; states=collected fields, recipients, trigger condition, consent control; evidence=vendor inventory, form version, privacy-policy change; assigned owner=tool lead; last verification date=2026-10-03; escalation=send to operations and technical leads when missing from inventory.
- Pressure scenario
- Support receives deletion, unsubscribe, or opt-out requests while the team wants to add remarketing audiences.
- Tempting move
- treat customer requests as a small support-inbox issue.
- Safer read
- customer rights requests test whether your data flow, vendor inventory, and response timing actually exist.
- First evidence
- Find request log, assigned owner, response template, admin path, and vendor deletion path first.
- Allowed move
- Only consider new data collection or remarketing after the request flow closes.
- Freeze rule
- Freeze new collection tools and remarketing audiences when customer requests have no assigned owner.
- Consent evidence record
- scope=deletion/unsubscribe/opt-out request; states=request log, admin path, vendor deletion path, response timing; evidence=ticket, email, admin log, vendor confirmation; assigned owner=support/privacy lead; last verification date=2026-10-03; escalation=move to incident response when no assigned owner exists.
Consent evidence record
Turn the consent evidence chain into a consent evidence record the team can review.
Do not reduce the record to “the banner works.” A useful record explains script inventory, four-state tests, reporting boundaries, the owner for customer-rights requests, and review cadence.
Consent evidence record
Consent sandbox, data-flow map, and DSAR practice record
Save the current choices as a local practice draft.
This saved record is a local practice draft, not valid consent, a compliance conclusion, or a live customer-request record. It captures the selected state sandbox, consent node, conflict case, pressure practice, and the governance fields you fill in. Use the current state, data purpose and regional branch, vendor recipient, and DSAR path to check whether the record is complete. Data stays in this browser and does not connect to, read, or modify Shopify, GA4, Google, Meta, email, customers, orders, accounts, vendors, or production data. Bring it to limited human review only after the quick check is correct and every field is filled. Saved, restored, or exported does not mean consent is valid, a request is complete, or launch is allowed.
No checkpoint finished in this lesson yet. Start with “Go to the exercise”.
Self-check not answered
FAQ
- When do I need privacy, cookie, and consent checks?
Use this workflow before installing a cookie banner, ad pixel, GA4, email popup, review app, heatmap tool, remarketing audience, or email automation. The core question is not whether a popup exists; it is what data you can collect, use, and keep using after the user chooses.
- If the user does not agree, can I still collect or use data?
Do not answer with one blanket yes or no. Separate necessary functionality, analytics, ads, email, and remarketing, then check Shopify Customer Privacy API, the cookie banner, Google Consent Mode v2, vendor scripts, and the relevant market boundary. Non-essential marketing tracking should not keep firing as if consent was granted after no choice or rejection.
- What does the consent conflict check inspect first?
It checks whether the visible symptom and hidden conflict match: banner exists but pixels fire early, email popup captures an address with unclear marketing permission, or Consent Mode repair lowers visible reporting. Each case starts with a four-state test, then records evidence, a named owner, the last verification date, and escalation path.
- Is a cookie banner enough for privacy and consent checks?
No. Test whether pixels, GA4, email popups, vendor scripts, and reporting notes actually change after first visit, reject, accept, withdraw, or opt out. A banner is the entry point, not the finish line.
- After Consent Mode repair, GA4 or ad conversions dropped. What should I do?
Check consent rate, ad_storage, analytics_storage, ad_user_data, ad_personalization, DebugView, Tag Assistant, and real Shopify orders first. If real orders did not drop in the same way, do not cut budget or rebuild the page only because visible platform conversions changed.
- How do I check whether Meta Pixel or Google tag fires before consent?
Run a clean-browser four-state test: first visit, reject, accept, and withdraw. Record Network, Tag Assistant, Pixel helper, browser storage, Customer Privacy API state, and GTM publish time.
- How should an email discount popup explain marketing consent?
Separate coupon delivery, order notices, and marketing email. Check form fields, double opt-in, unsubscribe link, deletion request path, and vendor inventory. If marketing consent is unclear, freeze new welcome flows, SMS, remarketing sync, and lookalike exports.
- What should the consent evidence record include?
Leave a consent evidence record: script firing, consent state, event gaps, privacy page, reporting boundary, customer rights, vendor inventory, a named owner, the last verification date, escalation path, and freeze scope. The next pixel, popup, or reporting review should not restart from guesswork.
Compliance paths after privacy and consent review
After consent review, route remaining market and EU questions to the matching path.
These links only help continue evidence-boundary checks. They do not approve a market, script, or tax treatment; review each item against the target market and current system.
Return to the Compliance Risk Hub
- Market-entry risk: complete the boundary evidence: If consent, tracking, or data use affects market entry, return to the market-risk map and confirm ownership and pause conditions field by field.
Sources
Public copy cites official checking paths.
This material does not provide legal conclusions. Official sources anchor Shopify settings, Customer Privacy API, Google Consent Mode v2, EDPB consent, ePrivacy, and EU online privacy checking boundaries.
Sources: 7Last checked
Shopify customer privacy settings (opens in a new tab)Checked
Google Consent Mode official guide (opens in a new tab)Checked
EDPB ePrivacy technical-scope guideline (opens in a new tab)Checked
EU online privacy cookies guidance (opens in a new tab)Checked
European Commission: data-subject requests (opens in a new tab)Checked